Performance Tips
Session Reuse for Performant REST Integration
Step 1: Initial Authentication
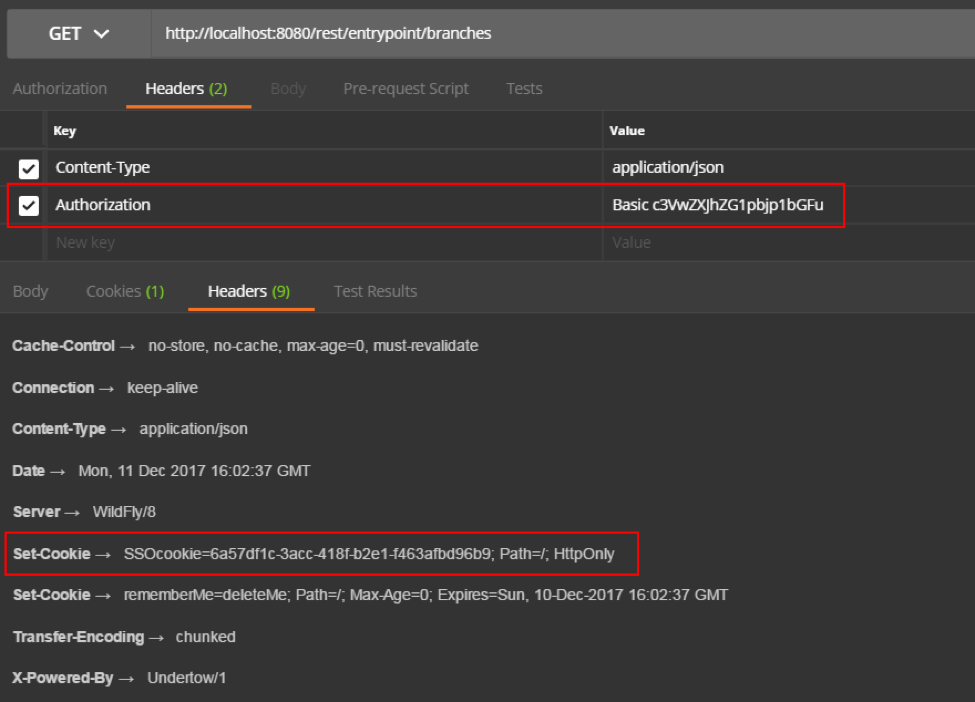
The first call to REST should have Basic Authentication added into the headers using the user and password created for it:
Authorization: Basic c3VwZXJhZG1pbjp1bGFu
Step 2: Get Session Cookie
The response to this first call will contain an attribute called Set-Cookie in its headers:
Set-Cookie: SSOcookie=de8d8de2-33d3-4bb7-9293-35e4636af3df
Step 3: Reuse Session
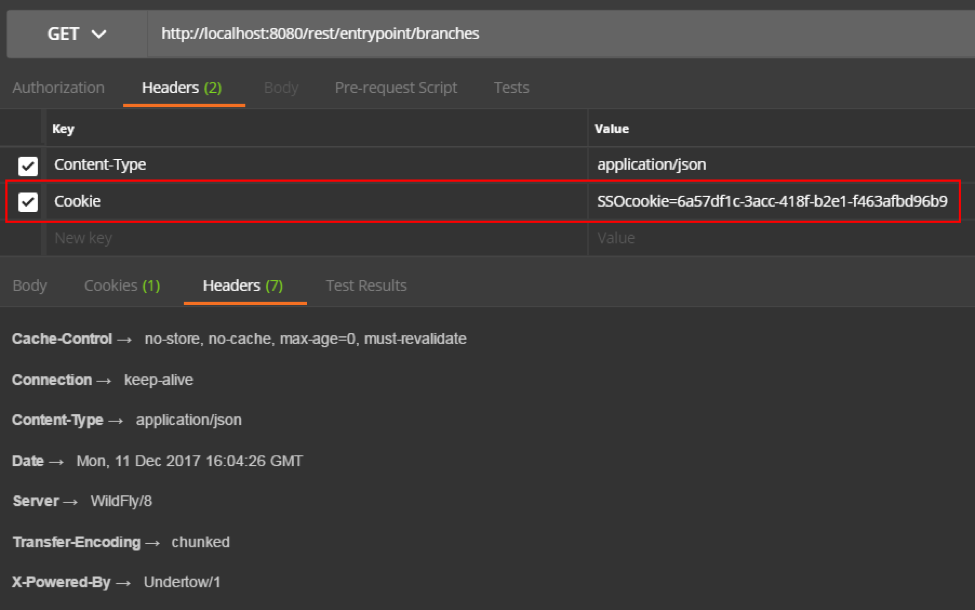
For subsequent calls, include the cookie in your request headers instead of Basic Authentication:
Cookie: SSOcookie=de8d8de2-33d3-4bb7-9293-35e4636af3df
This approach significantly improves performance by avoiding repeated authentication overhead.